Lead Fraud Prevention With Device and IP Fingerprinting
Stop paying for fake leads. Use device and IP fingerprinting to block fraud and protect your ROI. Call (510)-663-7016 to get started.
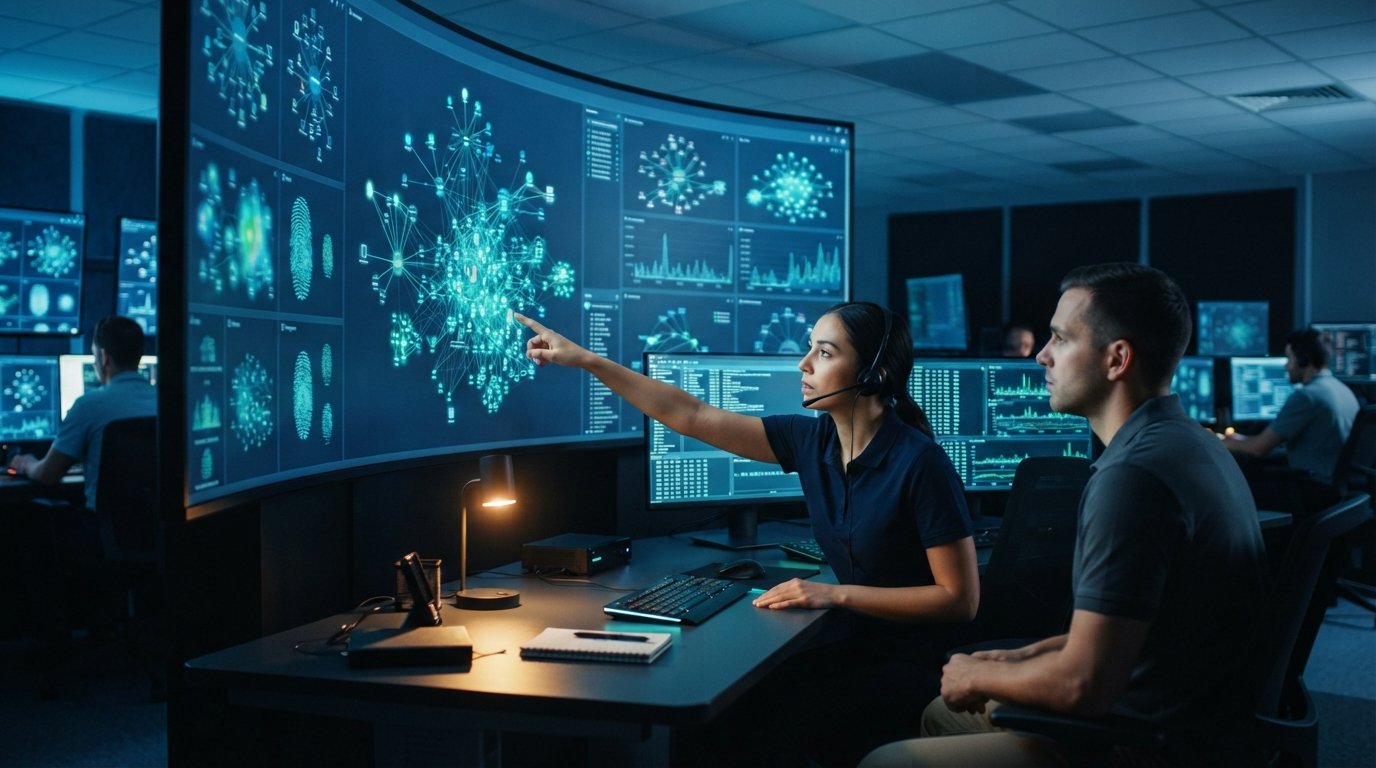
Every fraudulent lead that slips through your forms or call center costs you twice: once when you pay for it, and again when your sales team wastes hours chasing a dead end. In performance marketing, where margins are thin and competition is fierce, lead fraud prevention is not a nice-to-have; it is a survival requirement. Device and IP fingerprinting have emerged as two of the most powerful tools in that fight, giving advertisers and network owners a way to spot suspicious patterns before they drain budgets. This article explains how fingerprinting works, how to combine it with other verification layers, and how to avoid the false positives that can block legitimate traffic.
Why Lead Fraud Prevention Needs More Than Basic Validation
Traditional lead validation relies on simple checks: is the email formatted correctly? Does the phone number have the right number of digits? Is the ZIP code real? Fraudsters have long since learned to defeat these checks. They submit synthetic identities with valid-looking data, often using automated bots that can generate thousands of fake leads per hour. Others use human click farms to manually fill out forms with stolen or fabricated information. Basic validation cannot distinguish between a real consumer and a sophisticated fake.
That is where device and IP fingerprinting come in. These technologies look beyond the data the user submits and examine the context of the submission itself: the device making the request, the network it originates from, and the behavioral patterns surrounding the interaction. By analyzing these signals, you can identify anomalies that strongly correlate with fraud, even when the submitted data looks perfectly valid. The goal is not to block every unusual submission but to build a layered defense that catches fraud while letting genuine leads flow through.
For advertisers, the financial impact is direct. A single fraudulent lead in a mortgage or insurance vertical can cost hundreds of dollars, and at scale, fraud can consume a significant portion of a campaign budget. For network owners, fraud damages relationships with buyers and erodes trust in the entire supply chain. Preventing it requires a systematic approach that combines technology, process, and ongoing monitoring.
How Device Fingerprinting Exposes Fraudulent Submissions
Device fingerprinting collects a set of attributes about the device used to submit a lead: the operating system, browser type and version, screen resolution, installed fonts, time zone, language settings, and sometimes hardware characteristics like the graphics card or battery status. These attributes are combined into a unique identifier, or fingerprint, that can be used to recognize the same device across multiple submissions, even if the user clears cookies or uses a private browsing mode.
Fraudsters often reuse the same device to submit many fake leads. They might use a botnet, a single device with automated software, or a small set of devices rotated to avoid detection. Device fingerprinting exposes this behavior by revealing when multiple leads originate from the same physical device. For example, if fifty mortgage applications in a single hour all come from the same device fingerprint, that is a strong signal of fraud. Similarly, if a device fingerprint is associated with a known fraudulent history, you can block it preemptively.
Device fingerprinting is particularly effective against bot-driven fraud. Bots often run on servers or compromised machines with predictable characteristics, and they may not properly spoof all the attributes that fingerprinting collects. Even advanced bots that use headless browsers can leave telltale signs, such as missing plugins or inconsistent time zone settings. By analyzing these signals, you can flag automated submissions before they reach your buyers.
Combining Device Fingerprints With Behavioral Signals
Device fingerprinting becomes even more powerful when combined with behavioral analysis. How long did the user spend on the form? Did they fill it out in a suspiciously short time? Did they copy and paste the email address or phone number? Did they navigate directly to the form without visiting any other page? These behavioral signals, when correlated with device data, can dramatically improve fraud detection accuracy. A legitimate user typically exhibits a natural pattern of interaction, while a fraudster often shows rushed or mechanical behavior.
For call-based campaigns, device fingerprinting can be linked to call records. If the same device submits a web form and then makes a call from a different phone number, that mismatch can be a red flag. Conversely, if a device fingerprint is consistently associated with high-quality calls, you can use that signal to prioritize or approve traffic from that source.
The Role of IP Fingerprinting in Detecting Velocity and Duplication
IP fingerprinting focuses on the network address from which a lead originates. Every request to your form or call center carries an IP address, which can be analyzed for patterns. Simple IP checks might flag known proxies or VPNs, but advanced IP fingerprinting goes further by examining velocity, geolocation, and reputation.
IP velocity refers to the rate at which leads are submitted from a single IP address or a small range of addresses. A sudden spike in submissions from one IP is a classic sign of fraud. For instance, if a single IP submits twenty leads in ten minutes, that is almost certainly automated or coordinated fraud. Velocity checks can also be applied at the subnet level to catch distributed attacks that rotate through a block of IPs.
IP geolocation adds another layer. If a lead claims to be from New York but the IP address resolves to a data center in Eastern Europe, that discrepancy is worth investigating. While some legitimate users employ VPNs, a high concentration of mismatches from a particular traffic source suggests fraud. IP reputation databases can also flag addresses associated with known fraudulent activity, allowing you to block them automatically.
Duplicate detection ties IP and device signals together. By maintaining a history of submissions, you can identify when the same IP or device has been used to submit multiple leads with different personal information. This is a common fraud tactic: submitting the same lead repeatedly with slight variations to avoid simple duplicate checks. Fingerprinting makes these duplicates visible.
Building a Layered Defense: Fingerprinting Plus Verification
Device and IP fingerprinting are powerful on their own, but they are most effective when integrated into a layered fraud prevention strategy. No single signal is definitive, and relying on one method alone can lead to either missed fraud or excessive false positives. The best approach combines multiple signals to build a comprehensive risk profile for each lead.
Phone verification is a natural complement to fingerprinting. After a lead is submitted, an automated system can call the provided number to confirm that it is valid and that the person answering matches the submitted information. This catches fraudsters who use fake or disconnected numbers. For pay per call campaigns, call recordings and IVR systems add another layer: you can review calls for signs of fraud, such as a caller who cannot answer basic questions or who provides inconsistent information. When phone verification is combined with device and IP data, you create a robust defense that is difficult for fraudsters to penetrate.
Here is how a layered defense might look in practice:
- Real-time fingerprinting: Capture device and IP attributes at the point of submission and check them against known fraud signals.
- Velocity and duplication checks: Flag submissions that exceed reasonable thresholds for a single IP or device.
- Phone verification: Use automated calls or SMS to confirm the lead's phone number and identity.
- Behavioral analysis: Score submissions based on form interaction patterns and time spent.
- Post-submission review: For high-value leads, add manual review or call recording analysis.
Each layer catches different types of fraud, and together they create a system that is both sensitive and specific. The key is to calibrate thresholds carefully so that legitimate users are not inconvenienced. For example, you might set a higher velocity threshold for known and trusted publishers, while applying stricter rules to new or unproven sources.
Platforms like LeadGenerationPlatform offer built-in fraud prevention tools that incorporate many of these layers. Their Ping & Post and Pay Per Call models include call quality rules, repeat-caller limits, and publisher controls that help advertisers block low-quality traffic. Integrating device and IP fingerprinting into such a platform amplifies its effectiveness, giving you a single view of fraud risk across all channels.
Avoiding False Positives: Protecting Legitimate Traffic
One of the biggest challenges in fraud prevention is avoiding false positives. Blocking a fraudulent lead is a win, but blocking a legitimate customer is a loss. Overly aggressive fingerprinting rules can inadvertently flag shared IPs, public devices, or users with privacy-focused browsing habits. For example, many people use VPNs for legitimate privacy reasons, and some corporate networks route all employee traffic through a single IP. If you block every VPN or shared IP, you will lose real leads.
To mitigate false positives, adopt a risk-based approach rather than a binary block-or-allow model. Assign each lead a risk score based on the combined signals, and use that score to decide the appropriate action. Low-risk leads pass through automatically. Medium-risk leads might trigger additional verification, such as a phone call or a CAPTCHA. High-risk leads can be blocked or routed to a manual review queue. This graduated response ensures that you catch fraud without turning away good customers.
It is also important to monitor your false positive rate over time. Track how many leads are flagged and then later confirmed as legitimate. If a particular rule is causing too many false positives, adjust it. For instance, you might whitelist known corporate IP ranges or allow a certain number of submissions from shared devices before flagging. Continuous testing and refinement are essential to maintaining a balanced fraud prevention system.
Publishers play a critical role here. Approved publishers who send high-quality traffic should not be penalized by overly strict rules. Provide them with clear guidelines and tools to monitor their own traffic quality. When a publisher's traffic is flagged, investigate before taking action. Often, a conversation with the publisher can reveal whether the issue is fraud or simply a misunderstanding of the rules. Platforms that offer publisher controls and transparent reporting make this collaboration easier.
Publisher Controls That Keep Approved Traffic Flowing
Fraud prevention should not come at the expense of publisher relationships. Approved publishers are your partners in generating high-quality leads, and they need the tools and freedom to do their jobs effectively. A well-designed fraud prevention system includes publisher controls that allow for flexibility while maintaining oversight.
One important control is the ability to set custom rules per publisher. A trusted publisher with a long history of high-quality leads might be allowed higher velocity thresholds or exempted from certain checks. New publishers, on the other hand, might be subject to stricter scrutiny until they build a track record. This tiered approach rewards good behavior and isolates risk.
Transparency is another key factor. Publishers should have access to reports that show how their traffic is performing and whether any leads have been flagged. This allows them to identify and fix issues on their end, such as a poorly targeted ad campaign that is attracting low-quality traffic. When publishers can see the impact of their efforts, they are more likely to cooperate with fraud prevention measures.
Finally, provide clear channels for appeal. If a publisher believes their traffic has been wrongly flagged, they should be able to request a review. A human review process can catch errors and restore trust. By combining automated fingerprinting with human oversight, you create a system that is both efficient and fair.
For those looking to implement these strategies at scale, working with a platform that understands the nuances of lead fraud prevention is essential. AstoriaLeads, a sales lead provider and performance marketing platform, offers services such as Ping & Post lead distribution, Pay Per Call marketing, and phone verified leads, all designed to help businesses acquire high-quality customers while protecting against fraud. Their tools include call tracking, analytics, and integration support, making it easier to implement a layered defense.
Implementing Fingerprinting: Practical Steps
Ready to add device and IP fingerprinting to your fraud prevention stack? Start by evaluating your current capabilities. Do you have access to device and IP data at the point of lead capture? If not, you may need to integrate a fingerprinting solution into your forms or call tracking system. Many platforms offer APIs or JavaScript snippets that collect the necessary attributes.
Next, define your risk thresholds. Work with your data team to analyze historical leads and identify patterns associated with fraud. Use that analysis to set initial velocity limits, device reuse thresholds, and IP reputation rules. Then, implement a pilot program to test the rules on a subset of traffic. Monitor the results closely, tracking both fraud caught and false positives. Adjust as needed before rolling out more broadly.
Finally, integrate fingerprinting with your existing verification processes. If you use phone verification, feed the fingerprint data into the same decision engine so that all signals are considered together. This holistic view will give you the best results. Remember that fraud prevention is an ongoing process, not a one-time setup. Fraudsters adapt, and your defenses must adapt with them. Regular reviews and updates to your rules will keep your system effective.
For more detailed guidance on preventing specific types of fraud, such as form injection attacks, see our guide on how to prevent lead form injection fraud. Form injection is a related threat where fraudsters manipulate hidden fields or submit data directly to your endpoint, and fingerprinting can help detect it.
In conclusion, lead fraud prevention with device and IP fingerprinting is a powerful approach that combines technology and strategy to protect your campaigns. By understanding how these signals work, layering them with other verification methods, and carefully managing false positives, you can stop fraud without sacrificing legitimate leads. The investment in these tools pays off through higher ROI, cleaner data, and stronger partnerships with publishers. AstoriaLeads